FOD policies
Service Level Objectives
For latest information, refer to the Service Level Objectives defined in the Fortify on Demand Service Description.
All assessments have a target turnaround time represented by the Service Level Objectives (SLO) of the chosen assessment type. The SLO is specified in business days, based on the Fortify on Demand data center’s time zone. The generic Service Level Objectives are:
| Assessment type | Automated Audit | Security Expert Review |
|---|---|---|
| Static Assessment | Four (4) hours | 2 business days |
| Dynamic API Assessment | N/A | 2 business days |
| Dynamic Website Assessment | N/A | 2 business days |
If an assessment does not meet customary testing requirements, the testing team may pause the SLO timer while waiting for a response from the customer. The testing team is committed to promptly restarting the timer and testing as soon as possible.
If you have additional questions about SLOs and balancing your business timeline with an assessment service level, contact support.
Note: Service Level Agreements (SLAs) are specific contractual agreements with customers. The turnaround times may differ from defined SLOs. Service Level Agreements are defined in your customer statement of work (SOW) and include targets and liabilities if they are not met.
Service Level Objective Dates
The SLO start and end dates are defined as follows:
- Start Date: The date the application assessment was requested to be started
- End Date: The date the results are available
Service Level Objective Exceptions
For latest information, refer to the Service Level Objectives defined in the Fortify on Demand Service Description.
A static assessment SLO does not apply to any of the following exceptions:
- Application has not been packaged correctly as per Fortify on Demand best practice guidelines.
- The application payload exceeds 1,000 MB.
A dynamic or mobile assessment SLO does not apply to any of the following exceptions:
- Fortify on Demand is not provided continuous 24-hour per day access and fully operational test credentials to assess the application that is in scope.
- Fortify on Demand is not able to configure security testing tools to use a minimum of fifteen (15) concurrent connections continuously to assess a single application with an average response time of less than 600 ms to an HTTP/HTTPS request.
- Mobile binary is obfuscated or is not prepared as per Fortify on Demand best practice guidelines.
SCA scan time
The following is an approximate Fortify on Demand SCA scan time.
| Application Size | Approximate Fortify SCA Scan Time | Total Lines of Code (TLOC) |
|---|---|---|
| Extra Large | 12.6 hours | >1M |
| Large | 2.8 hours | >400K |
| Medium | 40 minutes | >100K |
| Small | 9 minutes | <100K |
Production Risk & Policy Compliance
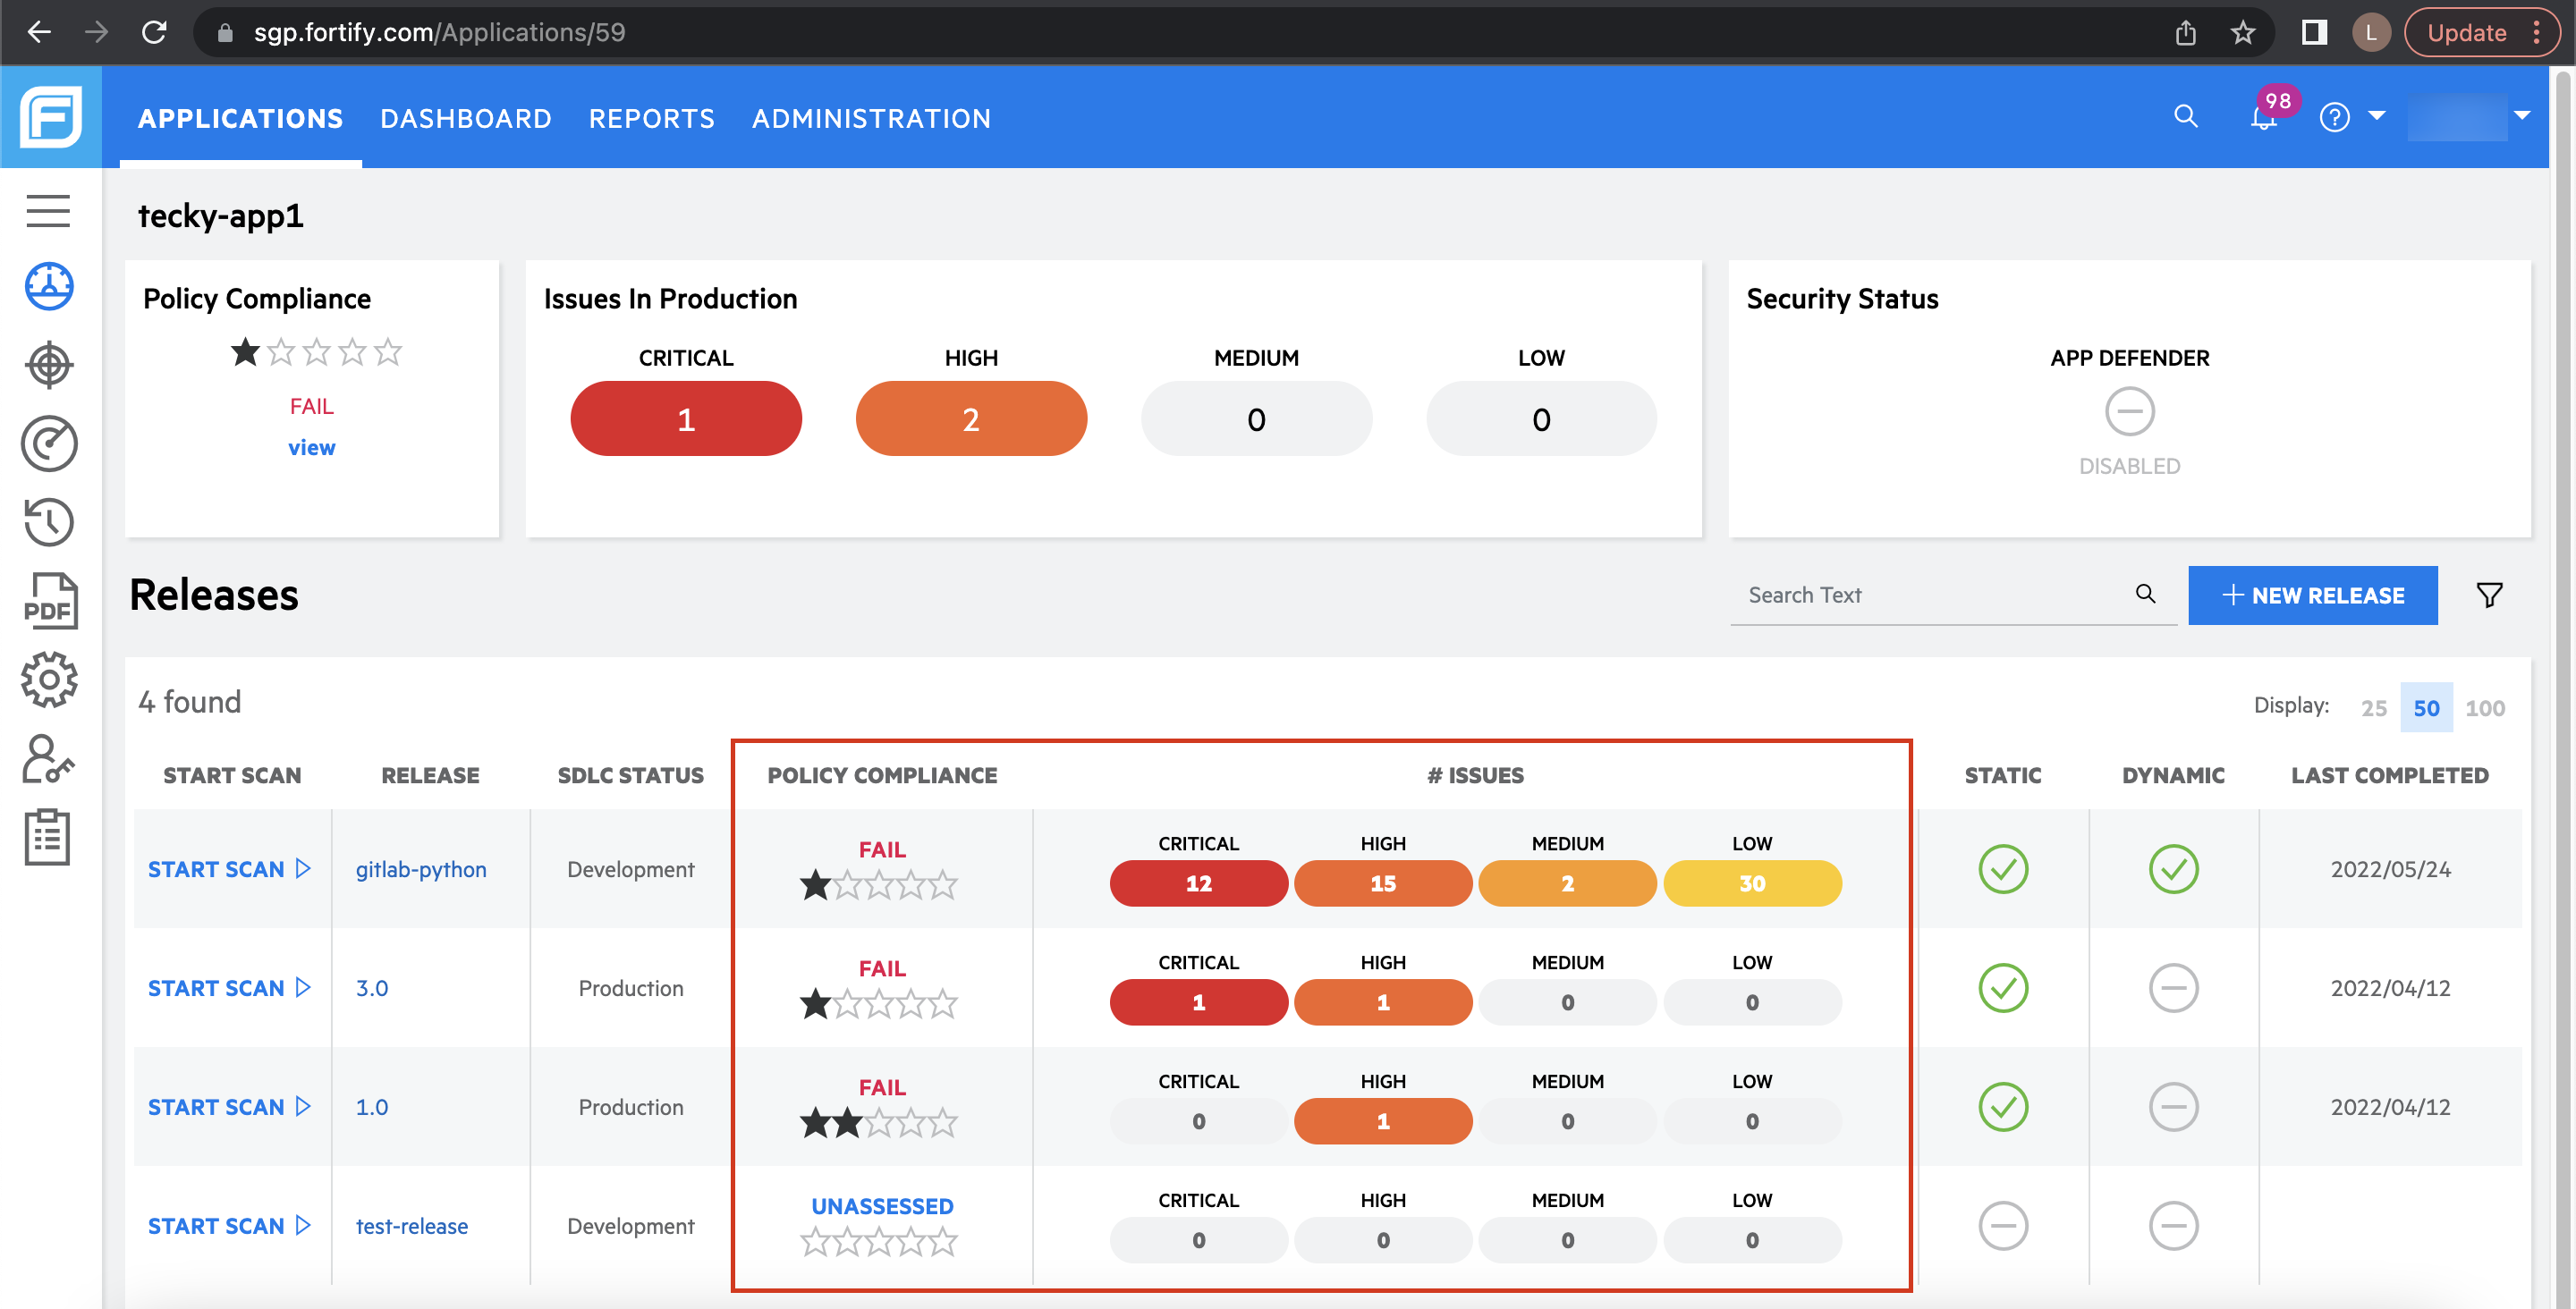
FOD introduces a system-wide policy that shows the severity of the findings for all FOD applications and their releases.
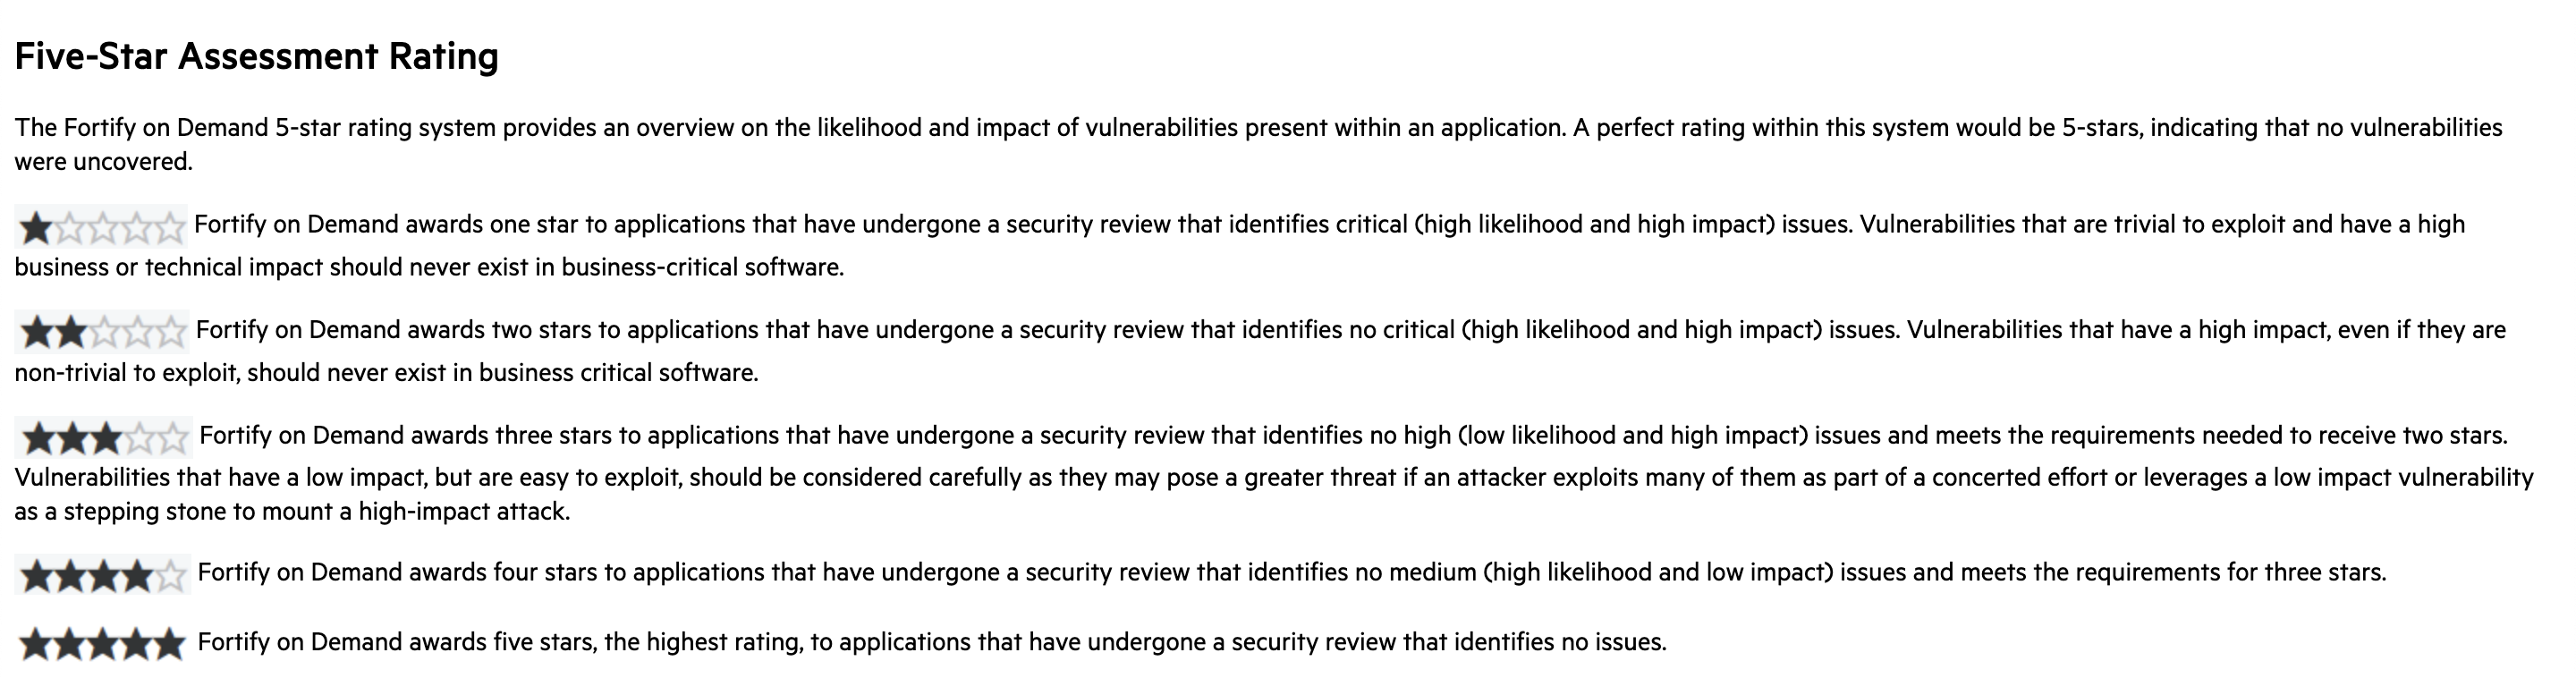
Five-star Assessment Rating
Releases are awarded 1-5 stars based on whether any CRITICAL, HIGH, MEDIUM, or LOW findings are found.
Security Policy
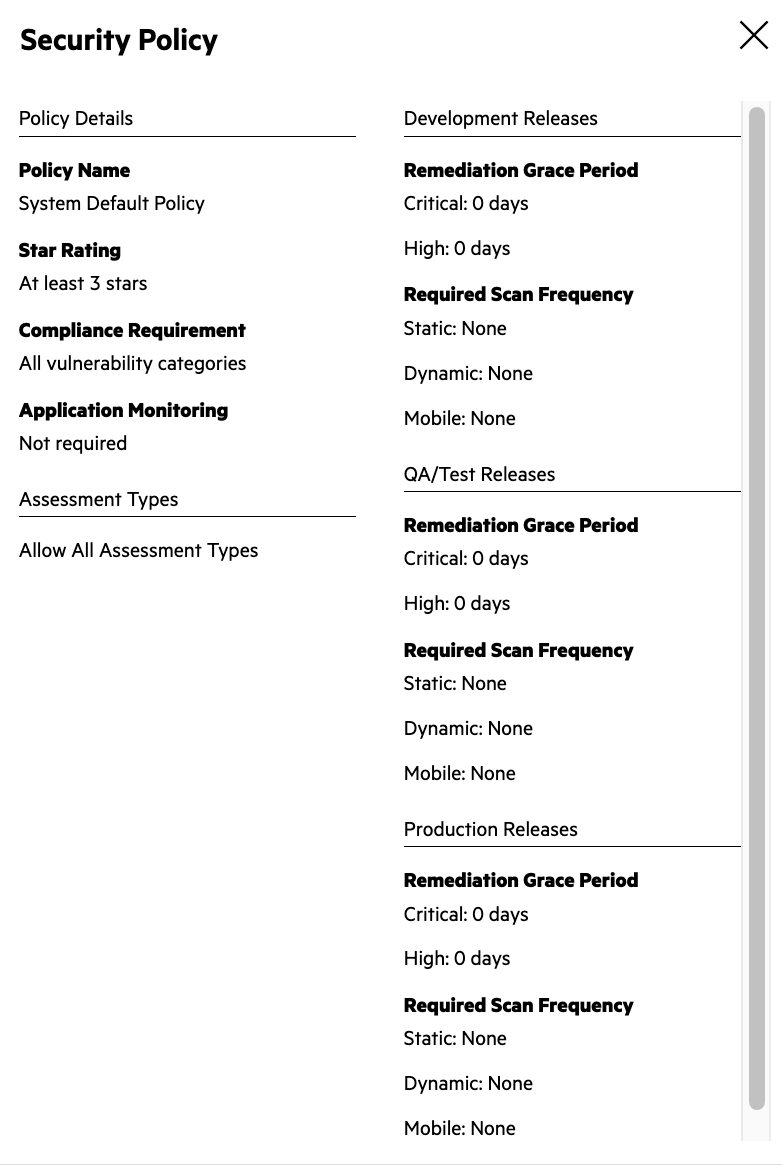
GovTech Security Policy uses System Default Policy. The details of the security policy are shown below, where Star Rating of the releases must be at least 3 Stars. This means that releases with HIGH issue(s) and above will fail.
Policy Compliance
Release that failed the security policy will have their Policy Compliance set to FAIL. This means that there are HIGH and above findings in that particular release.