Contribute SIEM rules
StackOps welcomes users to contribute to the Innersource SIEM framework.
To contribute to InnerSource:
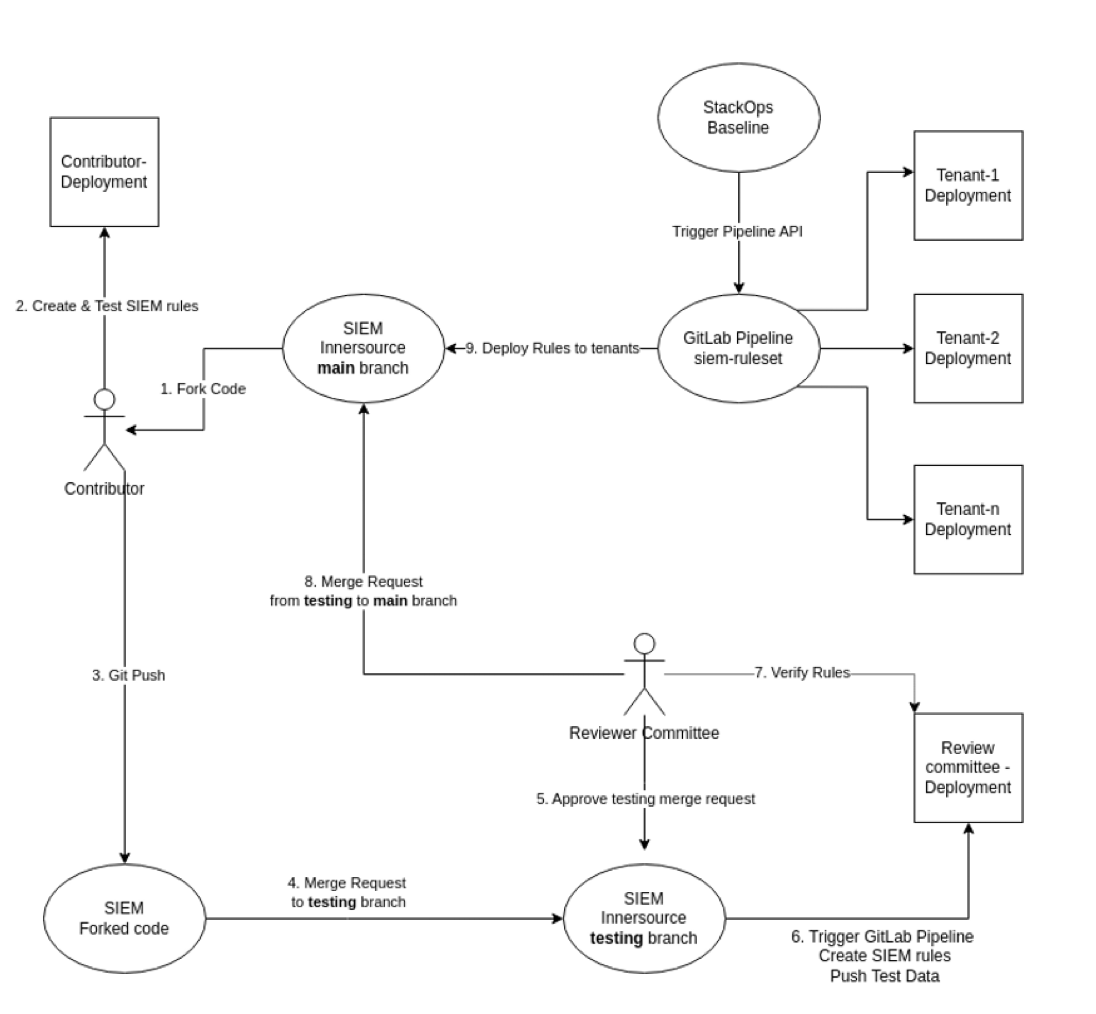
- Fork the code from the StackOps SIEM repository.
- Create and test the rules.
- Push your changes.
- Submit a merge request for approval to merge the changes into the testing branch.
To follow updates and new releases:
Star the repo to follow updates and new releases.
What is InnerSource?
InnerSource aims to foster collaboration, transparency, and innovation in our software development processes. It provides the following:
- Creates community to collaborate
- Scalability and flexibility with community input
- Contextual rules according to different projects
For more information, refer to Innersource in the Government.
SIEM InnerSource Framework
Security Information and Event Management (SIEM) collects logs and events, normalising this data for further analysis that can manifest as visualisations, alerts, searches, reports, and more. For more information, refer to Elastic documentation.
The following diagram depicts the InnerSource flow when you contribute SIEM rules.