Inherited GitLab group for GovTech subscriptions
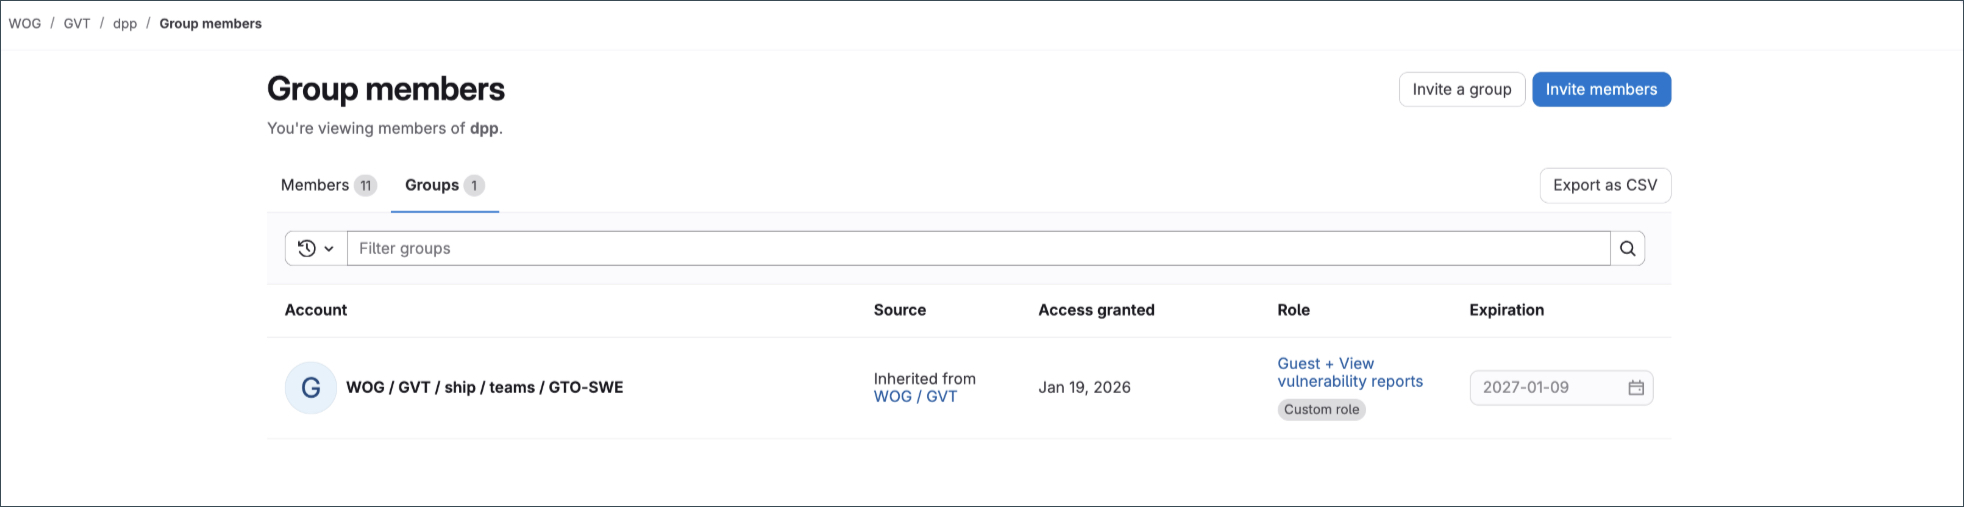
For all GitLab projects under GovTech subscriptions (WOG/GVT), the dedicated GTO-SWE group (WOG / GVT / ship / teams / GTO-SWE) is inherited automatically.
This group supports initiatives to uplift Software Engineering (SWE) practices across GovTech and has limited read access.
Scope
This access applies only to GovTech subscriptions (WOG/GVT namespace). It does not extend to other WOG agency subscriptions.
Purpose and benefits
The GTO SWE team has been granted limited access to GovTech subscriptions to support SWE practice uplift initiatives across GovTech.
This is intended to:
Analyse SWE practices: Perform analysis across GovTech projects based on dependency, licence, vulnerability, and project metadata — starting with dependency licence usage analysis — to identify opportunities for improvement and standardisation.
Support deeper dives with GovTech teams: As the team performs deeper analysis with GovTech teams, the scope may expand to additional SWE-related use cases.
Support data-informed improvements: Insights gathered may contribute to broader platform, workflow, and SWE practice improvement initiatives.
Roles and permissions granted
Users in this group are granted a Guest + View vulnerability reports custom role inherited from the WOG / GVT level.
The additional View vulnerability reports permission enables access to GitLab vulnerability and dependency-related reporting information, which may be used for dependency and licence analysis activities.
Privacy and security
The provisioned access is intended to be limited in scope and aligned with the analysis use cases described above.
The configured role is designed to provide more restricted access compared to broader project roles such as Reporter. However, the exact visibility and permissions available may depend on:
- GitLab feature visibility settings
- project visibility configuration
- inherited permissions
- future GitLab platform changes
Access review
Access is reviewed periodically and may be revoked earlier if there are role or work changes for the provisioned personnel.
Action required
No action is required. This access does not affect your project’s normal operations.
Questions or concerns?
If you have questions regarding this, contact us.
